Free PT0-001 sample questions
Real questions from the PenTest+ (v1) practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 6 of 12 free sample questions.
A penetration tester has been assigned to perform an external penetration assessment ofa company. Which ofthe following steps would BEST help with the passive-information-gathering process? (Choose two.)
A penetration tester has been asked to conduct a penetration test on a REST-based web service. Which ofthe following items is required?
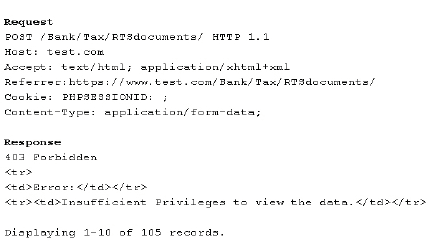
A penetration tester is testing a banking application and uncovers a vulnerability. The tester is logged in as a non-privileged user who should have no access to any data. Given the data below from the web interception proxy: Which ofthe following types ofvulnerabilities is being exploited?
A penetration tester has a full shell to a domain controller and wants to discover any user account that has not authenticated to the domain in 21 days. Which ofthe following commands would BEST accomplish this?
A penetration tester has compromised a Windows server and is attempting to achieve persistence. Which ofthe following would achieve that goal?
6 more free samples are waiting
Create a free account to unlock the whole PT0-001 sample bank, or get full access to all 138 practice questions in the simulator.