Free PT0-003 sample questions
Real questions from the PenTest+ (v3) practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
Which of the following explains the reason a tester would opt to use DREAD over PTES during the planning phase of a penetration test?
A penetration tester is performing a security review of a web application. Which of the following should the tester leverage to identify the presence of vulnerable open-source libraries?
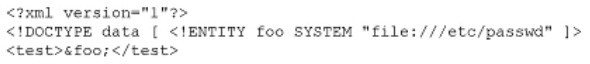
A penetration tester finds that an application responds with the contents of the /etc/passwd file when the following payload is sent:Which of the following should the tester recommend in the report to best prevent this type of vulnerability?
A penetration tester is assessing a financial technology company's cloud-native application, which is built on a Kubernetes cluster hosted in AWS. The engagement's goal is to simulate a full-chain attack starting from an external vulnerability. The tester first identifies a Server-Side Request Forgery (SSRF) vulnerability in a public-facing GraphQL endpoint running on a pod. This endpoint is used for generating PDF reports from user-supplied URLs. The pod is running in a default namespace on a worker node and does not have a specific IAM role attached. After exploiting the SSRF, the tester successfully queries the EC2 Instance Metadata Service (IMDSv1). The credentials retrieved belong to the worker node's instance profile, which has limited permissions, primarily for EC2 and ECR access. However, the tester discovers that the Kubelet API (port 10250) on the worker node allows anonymous authentication. Given this scenario, what is the MOST effective next step for the tester to escalate privileges from pod access to full control over the worker node? graph TD subgraph Internet Attacker[ Attacker ] end subgraph AWS VPC ALB[Application Load Balancer] subgraph Public Subnet GraphQL_Pod[GraphQL Pod SSRF Vulnerability ] end subgraph Private Subnet WorkerNode[EC2 Worker Node] KubeletAPI((Kubelet API Port 10250)) end end Attacker --> ALB --> GraphQL_Pod GraphQL_Pod -- SSRF --> IMDSv1[EC2 Metadata Service] GraphQL_Pod -- SSRF --> KubeletAPI KubeletAPI -- controls --> WorkerNode
A penetration tester is evaluating an AI-powered image recognition system used for physical access control at a secure data center. The system is designed to grant access only to authorized personnel. The tester's objective is to cause the model to misclassify a photo of an unauthorized individual as an authorized employee, thereby gaining entry. The tester has black-box access to the system's API but no knowledge of the model's architecture or training data. Which type of adversarial machine learning attack is the tester attempting to perform?
A DevOps team is building a CI/CD pipeline and wants to automate the process of identifying known vulnerabilities within the open-source libraries and third-party dependencies used in their containerized application. The goal is to fail the build if a dependency with a critical CVE is detected. Which of the following security testing methodologies should be integrated into the pipeline to achieve this specific goal?
A penetration tester is assessing a web application with a strict Content Security Policy (CSP). The tester finds a reflected XSS vulnerability but cannot execute inline scripts. The application's CSP header is as follows: `Content-Security-Policy: default-src 'self'; script-src 'self' https://trusted.cdn.com; object-src 'none'; style-src 'self' 'unsafe-inline';` Which TWO of the following techniques could be used to bypass this CSP and execute arbitrary JavaScript? (Select TWO).
While conducting a scheduled penetration test against a client's external network, a consultant discovers evidence of an active, ongoing compromise by an unknown threat actor. The consultant identifies a live command-and-control (C2) beaconing out from a critical web server. According to the rules of engagement, all critical findings must be reported within 24 hours. What is the MOST appropriate immediate action for the consultant to take?
An automated vulnerability scan reports a high-severity 'Unquoted Service Path' vulnerability on a Windows Server. The finding indicates that the service 'CustomSvc' has the path `C:\Program Files\Custom App\service.exe`. Before confirming this as an exploitable vulnerability, what is the MOST critical next step for the penetration tester to perform for manual validation?
10 more free samples are waiting
Create a free account to unlock the whole PT0-003 sample bank, or get full access to all 305 practice questions in the simulator.