Free CS0-003 sample questions
Real questions from the Cybersecurity Analyst (CySA+ v3) practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 15 of 30 free sample questions.
Which of the following tools would work best to prevent the exposure of PII outside of an organization?
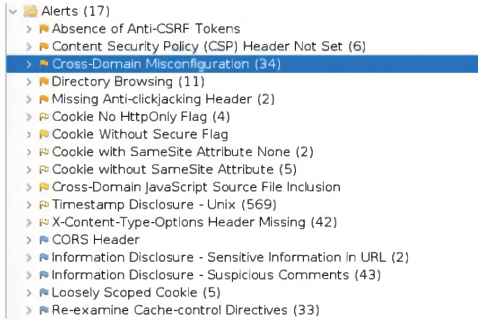
An organization conducted a web application vulnerability assessment against the corporate website, and the following output was observed:Which of the following tuning recommendations should the security analyst share?
Which of the following items should be included in a vulnerability scan report? (Choose two.)
The Chief Executive Officer of an organization recently heard that exploitation of new attacks in the industry was happening approximately 45 days after a patch was released. Which of the following would best protect this organization?
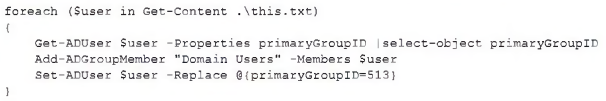
A security analyst recently joined the team and is trying to determine which scripting language is being used in a production script to determine if it is malicious. Given the following script:Which of the following scripting languages was used in the script?
A company's user accounts have been compromised. Users are also reporting that the company's internal portal is sometimes only accessible through HTTP, other times; it is accessible through HTTPS. Which of the following most likely describes the observed activity?
A security analyst is tasked with prioritizing vulnerabilities for remediation. The relevant company security policies are shown below:Security Policy 1006: Vulnerability Management1. The Company shall use the CVSSv3.1 Base Score Metrics (Exploitability and Impact) to prioritize the remediation of security vulnerabilities.2. In situations where a choice must be made between confidentiality and availability, the Company shall prioritize confidentiality of data over availability of systems and data.3. The Company shall prioritize patching of publicly available systems and services over patching of internally available system.According to the security policy, which of the following vulnerabilities should be the highest priority to patch?
Which of the following will most likely ensure that mission-critical services are available in the event of an incident?
The Chief Information Security Officer wants to eliminate and reduce shadow IT in the enterprise. Several high-risk cloud applications are used that increase the risk to the organization. Which of the following solutions will assist in reducing the risk?
A security analyst is reviewing a new cloud architecture proposal that utilizes a dedicated secure access layer to connect users to applications. The architecture combines SD-WAN capabilities with comprehensive security functions such as SWG, CASB, FWaaS, and ZTNA, delivered primarily as a service. Which of the following terms BEST describes this architecture? graph LR User[Remote User] -->|Encrypted Tunnel| Edge[Cloud Edge] Branch[Branch Office] -->|SD-WAN| Edge subgraph SASE_Cloud [Security Cloud] Edge --> FWaaS Edge --> CASB Edge --> DLP Edge --> ZTNA end ZTNA --> SaaS[SaaS Apps] ZTNA --> IaaS[IaaS/PaaS] FWaaS --> Internet
During a vulnerability scan analysis, an analyst identifies a critical finding on a legacy server. The vulnerability allows remote code execution (RCE) but requires the attacker to have an existing low-privileged user account on the system. The server is located in a segmented VLAN with no direct internet access. When calculating the CVSS v3.1 score to prioritize this vulnerability, which Attack Vector (AV) metric should be selected?
15 more free samples are waiting
Create a free account to unlock the whole CS0-003 sample bank, or get full access to all 271 practice questions in the simulator.