Free CS0-002 sample questions
These free CS0-002 sample questions come from our practice test for the retired CySA+ v2, with answers and explanations. They cover vulnerability scans, log analysis and incident response. Candidates booking CySA+ today should switch to CS0-004.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 6 of 12 free sample questions.
A security analyst received a SIEM alert regarding high levels of memory consumption for a critical system. After several attempts to remediate the issue, the system went down. A root cause analysis revealed a bad actor forced the application to not reclaim memory. This caused the system to be depleted of resources. Which of the following BEST describes this attack?
Which of the following software security best practices would prevent an attacker from being able to run arbitrary SQL commands within a web application? (Choose two.)
A cyber-incident response analyst is investigating a suspected cryptocurrency miner on a company's server. Which of the following is the FIRST step the analyst should take?
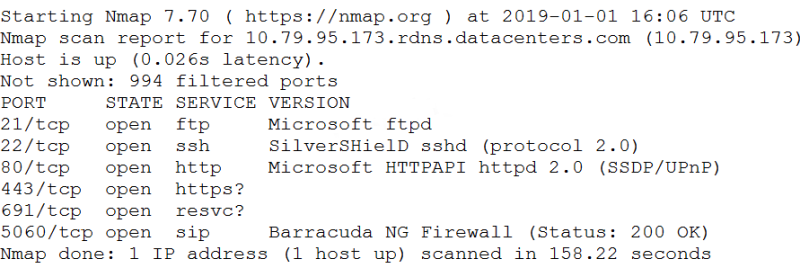
An information security analyst is compiling data from a recent penetration test and reviews the following output: The analyst wants to obtain more information about the web-based services that are running on the target. Which of the following commands would MOST likely provide the needed information?
A compliance officer of a large organization has reviewed the firm's vendor management program but has discovered there are no controls defined to evaluate third-party risk or hardware source authenticity. The compliance officer wants to gain some level of assurance on a recurring basis regarding the implementation of controls by third parties. Which of the following would BEST satisfy the objectives defined by the compliance officer? (Choose two.)
6 more free samples are waiting
Create a free account to unlock the whole CS0-002 sample bank, or get full access to all 543 practice questions in the simulator.