Free 312-50v10 sample questions
Each free 312-50v10 sample question below follows the retired CEH v10 syllabus and comes with the answer and an explanation. Questions span scanning, system hacking and web attacks. For the current exam, use the 312-50v13 sample questions.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
Which of the following is considered as one of the most reliable forms of TCP scanning?
Which of the following scanning method splits the TCP header into several packets and makes it difficult for packet filters to detect the purpose of the packet?
Which of the following is the BEST way to defend against network sniffing?
You have successfully gained access to a Linux server and would like to ensure that the succeeding outgoing traffic from this server will not be caught by Network-Based Intrusion Detection Systems (NIDS). What is the best way to evade the NIDS?
What is the purpose of a demilitarized zone on a network?
You need to deploy a new web-based software package for your organization. The package requires three separate servers and needs to be available on the Internet. What is the recommended architecture in terms of server placement?
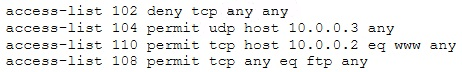
The security administrator of ABC needs to permit Internet traffic in the host 10.0.0.2 and UDP traffic in the host 10.0.0.3. He also needs to permit all FTP traffic to the rest of the network and deny all other traffic. After he applied his ACL configuration in the router, nobody can access to the ftp, and the permitted hosts cannot access the Internet. According to the next configuration, what is happening in the network?
When conducting a penetration test, it is crucial to use all means to get all available information about the target network. One of the ways to do that is by sniffing the network. Which of the following cannot be performed by the passive network sniffing?
A company's Web development team has become aware of a certain type of security vulnerability in their Web software. To mitigate the possibility of this vulnerability being exploited, the team wants to modify the software requirements to disallow users from entering HTML as input into their Web application. What kind of Web application vulnerability likely exists in their software?
10 more free samples are waiting
Create a free account to unlock the whole 312-50v10 sample bank, or get full access to all 2,181 practice questions in the simulator.