Free SY0-501 sample questions
Each free SY0-501 sample question below is drawn from our practice test for the retired Security+ exam, with an answer and explanation. They cover attacks, identity and access, and cryptography. Anyone booking Security+ now needs SY0-701 instead.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 11 of 22 free sample questions.
A security analyst wishes to increase the security of an FTP server. Currently, all traffic to the FTP server is unencrypted. Users connecting to the FTP server use a variety of modern FTP client software. The security analyst wants to keep the same port and protocol, while also still allowing unencrypted connections. Which of the following would BEST accomplish these goals?
Which of the following explains why vendors publish MD5 values when they provide software patches for their customers to download over the Internet?
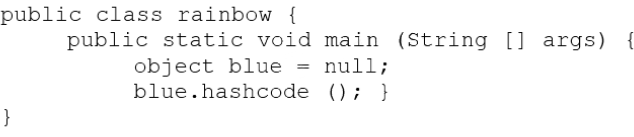
Refer to the following code below. Which of the following vulnerabilities would occur if this is executed?
Multiple employees receive an email with a malicious attachment that begins to encrypt their hard drives and mapped shares on their devices when it is opened. The network and security teams perform the following actions: Shut down all network shares. Run an email search identifying all employees who received the malicious message. Reimage all devices belonging to users who opened the attachment. Next, the teams want to re-enable the network shares. Which of the following BEST describes this phase of the incident response process?
An organization has determined it can tolerate a maximum of three hours of downtime. Which of the following has been specified?
Which of the following types of keys is found in a key escrow?
An auditor wants to test the security posture of an organization by running a tool that will display the following: Which of the following commands should be used?
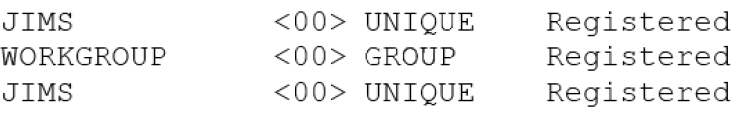
Which of the following encryption methods does PKI typically use to securely protect keys?
An organization is using a tool to perform a source code review. Which of the following describes the case in which the tool incorrectly identifies the vulnerability?
When performing data acquisition on a workstation, which of the following should be captured based on memory volatility? (Choose two.)
11 more free samples are waiting
Create a free account to unlock the whole SY0-501 sample bank, or get full access to all 1,483 practice questions in the simulator.