Free NSE4_FGT-6.2 sample questions
Real questions from the Fortinet NSE4 - FortiOS 6.2 practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 6 of 12 free sample questions.
How does FortiGate verify the login credentials of a remote LDAP user?
Which statement about the firewall policy authentication timeout is true?
By default, when logging to disk, when does FortiGate delete logs?
Which two statements about conserve mode are true? (Choose two.)
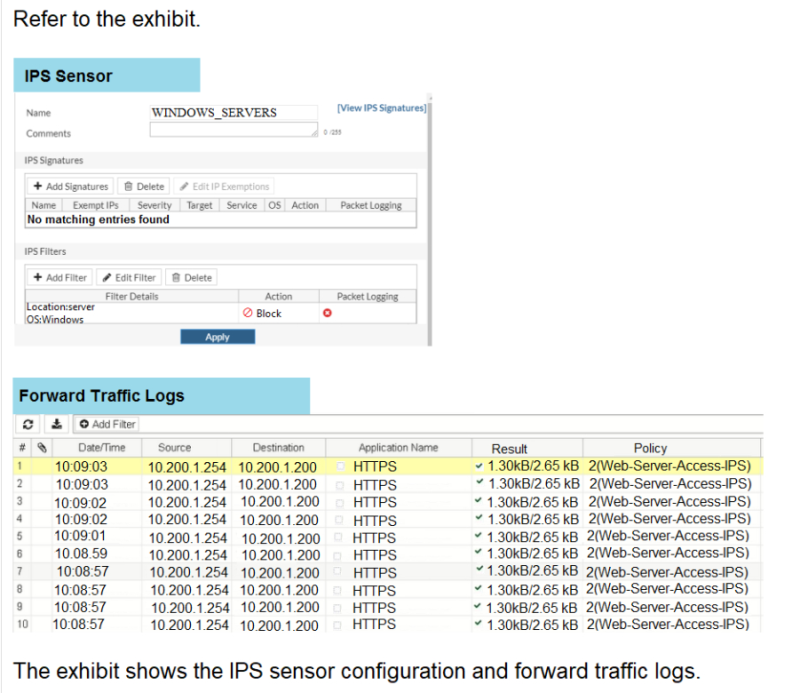
An administrator has configured the WINDOWS_SERVERS IPS sensor in an attempt to determine whether the influx of HTTPS traffic is an attack attempt, or not. After applying the IPS sensor, FortiGate is still not generating any IPS logs for the HTTPS traffic. What is a possible reason for this?
6 more free samples are waiting
Create a free account to unlock the whole NSE4_FGT-6.2 sample bank, or get full access to all 125 practice questions in the simulator.