Free ECSAv10 sample questions
Below are free ECSAv10 sample questions with answers and explanations. The set runs from scoping to network testing and web flaws such as SQL injection. Check how you would order each step of a real test.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
Peter, a disgruntled ex-employee of Zapmaky Solutions Ltd., is trying to jeopardize the company’s website http://zapmaky.com. He conducted the port scan of the website by using the Nmap tool to extract the information about open ports and their corresponding services. While performing the scan, he recognized that some of his requests are being blocked by the firewall deployed by the IT personnel of Zapmaky and he wants to bypass the same. For evading the firewall, he wanted to employ the stealth scanning technique which is an incomplete TCP three-way handshake method that can effectively bypass the firewall rules and logging mechanisms. Which if the following Nmap commands should Peter execute to perform stealth scanning?
Richard, a penetration tester was asked to assess a web application. During the assessment, he discovered a file upload field where users can upload their profile pictures. While scanning the page for vulnerabilities, Richard found a file upload exploit on the website. Richard wants to test the web application by uploading a malicious PHP shell, but the web page denied the file upload. Trying to get around the security, Richard added the ‘jpg’ extension to the end of the file. The new file name ended with ‘.php.jpg’. He then used the Burp suite tool and removed the ‘jpg’’ extension from the request while uploading the file. This enabled him to successfully upload the PHP shell. Which of the following techniques has Richard implemented to upload the PHP shell?
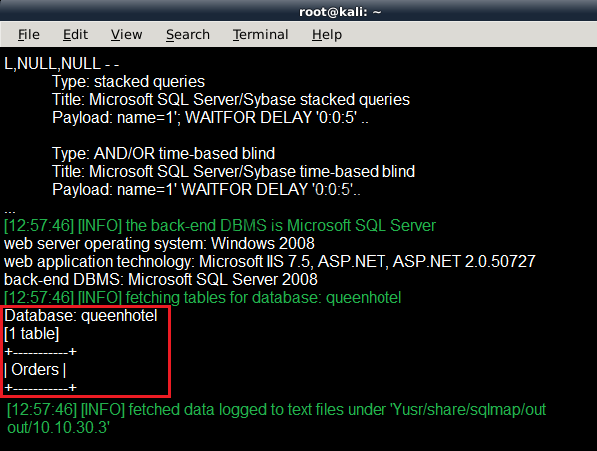
Richard is working on a web app pen testing assignment for one of his clients. After preliminary information, gathering and vulnerability scanning Richard runs the SQLMAP tool to extract the database information. Which of the following commands will give Richard an output as shown in the screenshot?
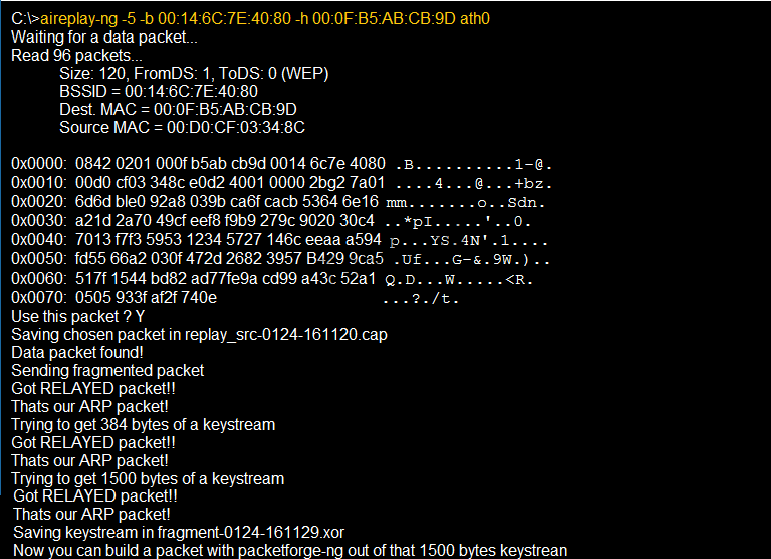
Identify the PRGA from the following screenshot:
James is an attacker who wants to attack XYZ Inc. He has performed reconnaissance over all the publicly available resources of the company and identified the official company website http://xyz.com. He scanned all the pages of the company website to find for any potential vulnerabilities to exploit. Finally, in the user account login page of the company’s website, he found a user login form which consists of several fields that accepts user inputs like username and password. He also found than any non-validated query that is requested can be directly communicated to the active directory and enable unauthorized users to obtain direct access to the databases. Since James knew an employee named Jason from XYZ Inc., he enters a valid username “jason and injects “jason)) in the username field. In the password field, James enters “blah and clicks Submit button. Since the complete URL string entered by James becomes “USER=jason))(PASS=blah)), only the first filter is processed by the Microsoft Active Directory, that is, the query “USER=jason)) is processed. Since this query always stands true, James successfully logs into the user account without a valid password of Jason. In the above scenario, identify the type of attack performed by James?
An organization has deployed a web application that uses encoding technique before transmitting the data over the Internet. This encoding technique helps the organization to hide the confidential data such as user credentials, email attachments, etc. when in transit. This encoding technique takes 3 bytes of binary data and divides it into four chunks of 6 bits. Each chunk is further encoded into respective printable character. Identify the encoding technique employed by the organization?
During an internal network audit, you are asked to see if there is any RPC server running on the network and if found, enumerate the associate RPC services. Which port would you scan to determine the RPC server and which command will you use to enumerate the RPC services?
The penetration testing team of MirTech Inc. identified the presence of various vulnerabilities in the web application coding. They prepared a detailed report addressing to the web developers regarding the findings. In the report, the penetration testing team advised the web developers to avoid the use of dangerous standard library functions. They also informed the web developers that the web application copies the data without checking whether it fits into the target destination memory and is susceptible in supplying the application with large amount of data. According to the findings by the penetration testing team, which type of attack was possible on the web application?
A penetration tester is attempting to bypass a network firewall that performs stateful packet inspection but does not perform deep packet inspection on DNS traffic. The tester has established a foothold on a compromised machine inside the network. The goal is to exfiltrate a small file containing sensitive data. Which of the following techniques would be most effective for bypassing the firewall under these specific conditions? graph TD Attacker[Attacker C2] -- Internet -- FW[Firewall] subgraph Internal Network CompromisedHost[Compromised Host] DNSServer[Internal DNS Server] end FW -- Allows Port 53 --> DNSServer CompromisedHost -- Exfiltration Tunnel --> DNSServer
10 more free samples are waiting
Create a free account to unlock the whole ECSAv10 sample bank, or get full access to all 396 practice questions in the simulator.